
A penetration testing team you can check
Tester certifications are shared on request and client references are available under NDA. This page shows what else you can check before you sign.
For your vendor file
| Company | EU-based. Legal entity details are in our privacy policy. |
|---|---|
| Team | 25 certified senior pentesters, employees and subcontractors |
| Clients | Worldwide, including the US and UK |
| Insurance | Professional indemnity insurance |
| Invoicing | USD, EUR or GBP |
| Reports | English by default; other languages can be discussed |
OSCP, OSCE, CISSP, CEH, CISA, CISM, CRISC, CCNA, CCNP, ISO/IEC 27001 Lead Auditor
Certifications our testers hold. See the full list.
Certified senior pentesters
Executed penetration tests
Years of offensive security ops
%
Of reported findings manually verified
What kind of company is Pentestica?
Pentestica is an EU-based penetration testing company with a team of 25 certified senior pentesters and clients worldwide, including the US and UK. We test web applications, APIs, mobile apps, cloud and network infrastructure, and smart contracts, and run red team and TLPT engagements. Every reported finding is manually verified. Our testing is aligned with OWASP, PTES and NIST SP 800-115, and each project ends with a management summary and a technical report, and a retest is available after your fixes.
Our core discipline is offensive security testing carried out by people. Tools help with reconnaissance and coverage, but every vulnerability in our reports has been exploited or confirmed by hand, with evidence your developers can reproduce.

How can you verify Pentestica before you sign?
Everything you can check, where you check it and when.
| What to check | Where |
|---|---|
| Open now | |
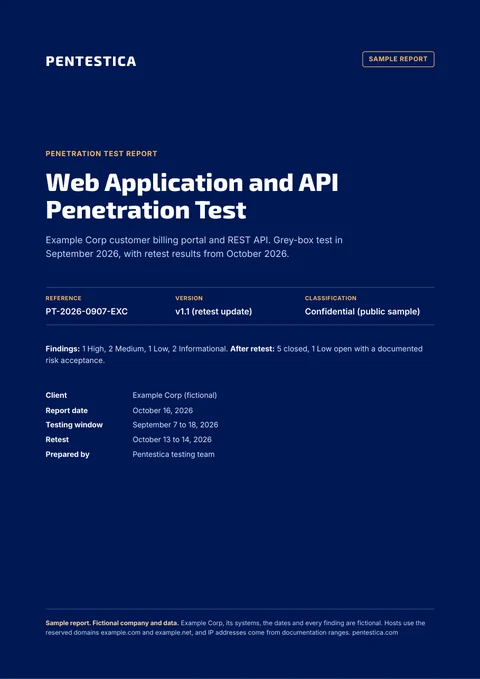
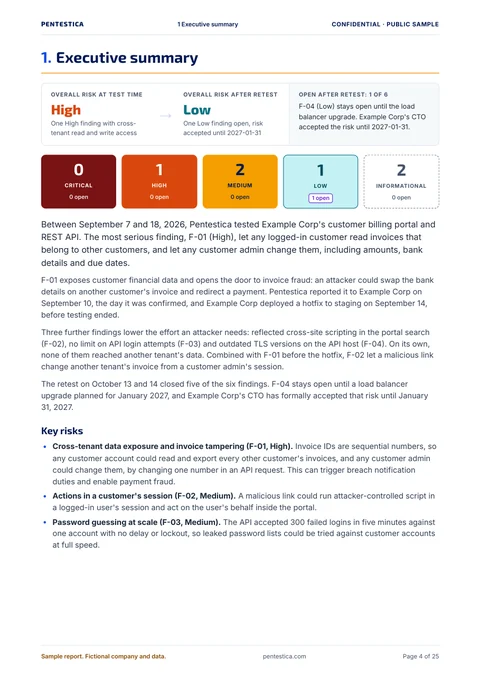
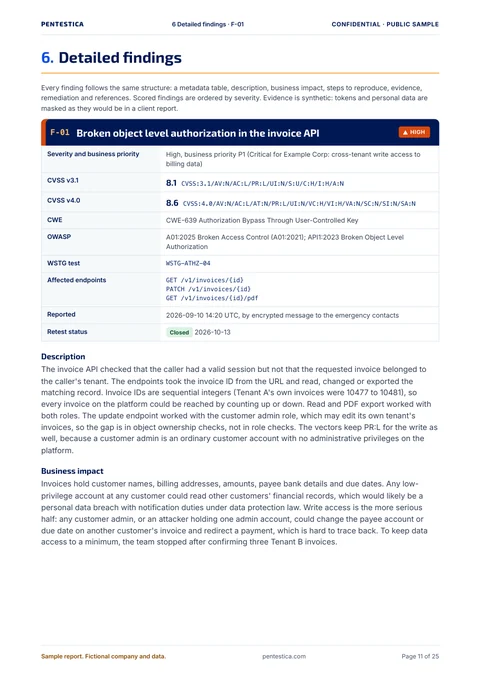
| Sample penetration test report | 25 pages, no email required |
| Case studies from real engagements | Case studies page |
| Published price ranges | Pricing page |
| Cost benchmarks by test type | Benchmarks page |
| Our security contact file | security.txt |
| With your quote | |
| Fixed price for the agreed scope; work outside that scope can cost more | In writing, in your quote |
| Targets, test type and tester-days | In your written scope |
| Rules of engagement and testing windows | In your written scope |
| Start date and retest terms | Agreed with your quote |
| On request | |
| Tester certifications | Shared on request |
| Subcontractor list | Shared on request |
| NDA | Before you share details |
| Client references | Under NDA |
| In the contract | |
| Data processing agreement (DPA) | In your contract |
| BAA | When US medical data is in scope |
| Governing law | Set out in the contract |
| A different data retention period | In your contract, if you need one |
Who tests your systems?

Your project is run by senior pentesters from our team of 25, backed by more than 10 years of offensive security operations and more than 500 executed penetration tests. Our testers hold certifications including OSCP, OSCE, CISSP, CEH, CISA, CISM, CRISC, CCNA, CCNP and ISO/IEC 27001 Lead Auditor.
Employment
Employees and subcontractors. Clients can get the subcontractor list on request.
References
Under NDA. Certifications on request.
Tester-days
Your written scope states how many.
Which certificates do testers hold?
Tester certifications can be shared on request, if your procurement or audit process requires them.
Testing and consulting
- OSCPOffensive Security Certified Professional
- OSCEOffensive Security Certified Expert
- CEHCertified Ethical Hacker
- CSCCertified Security Consultant
Security, audit and risk
- CISSPCertified Information Systems Security Professional
- CISACertified Information Systems Auditor
- CISMCertified Information Security Manager
- CRISCCertified in Risk and Information Systems Control
Standards and networks
- ISO/IEC 27001 LAInformation security management system Lead Auditor
- BCCLABusiness Continuity Certified Lead Auditor
- CCNACisco Certified Network Associate
- CCNPCisco Certified Network Professional
CISSP Certified Information Systems Security Professional
How do we handle your data?
We collect only what’s needed as evidence, keep it encrypted on servers in the EU and delete it on a fixed schedule.
After the report or retest, evidence and working notes are deleted.
In writing
We confirm deletion in writing. A different period can be set in your contract.
Collected, stored, access, delivery, credentials, contracts
| Collected | Only what’s needed as evidence. No copies of production databases. Personal data in evidence is masked. |
|---|---|
| Stored | Encrypted tester laptops, a separate encrypted vault for each project and servers in the EU. No personal cloud accounts and no public AI tools. |
| Access | Only people on the project, with MFA and access logging. |
| Report delivery | Never by plain email. You get an encrypted link or file, and the password travels through a different channel. |
| Your credentials | Stored separately and encrypted, then deleted when the test ends. You disable the test accounts. |
| Contracts | NDA and data processing agreement (DPA), plus a BAA when US medical data is in scope. |
How does a Pentestica engagement work?
Every engagement follows the same four stages, whether we are testing a single API or running a multi-week red team operation. How we set the rules of engagement.
Scoping
We agree in writing on the targets, test type (black, grey or white box), rules of engagement, testing windows and tester-days. You know the cost before testing starts.
Testing
Certified pentesters map your attack surface, exploit vulnerabilities by hand and chain small weaknesses into real attack paths. Critical issues are reported during the test.
Reporting
A typical test takes one to three weeks, plus a few days for the report. Every finding has evidence of exploitation, a business impact rating and step-by-step remediation.
Retest
Once your team has applied the fixes, a retest is available to confirm which issues are closed.
What makes the report different?
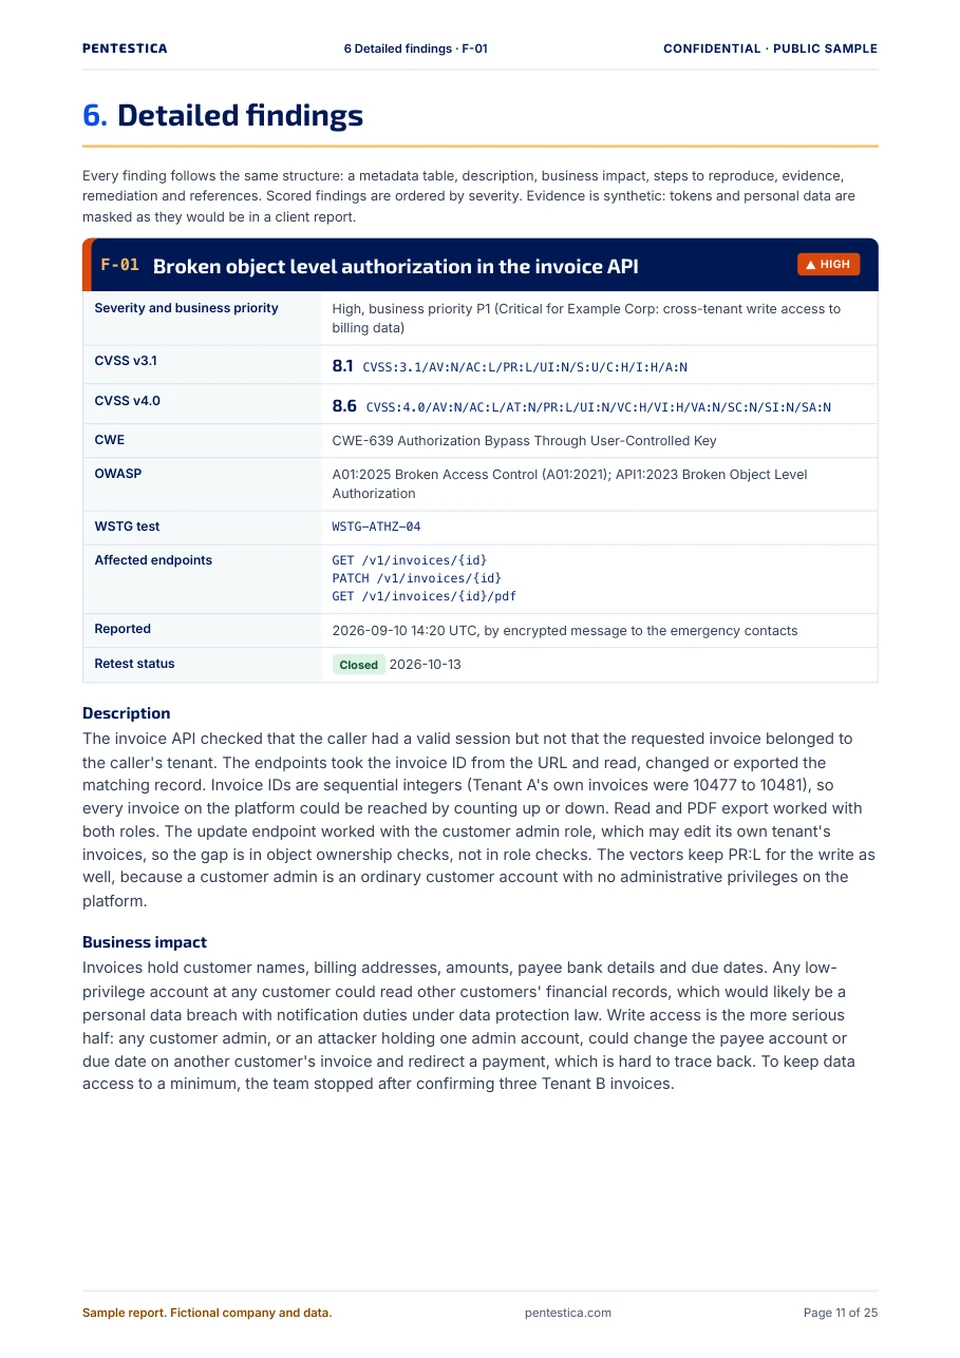
Every finding is checked by hand
Scanners match known patterns, but they can’t judge business logic or chain small weaknesses into a real attack path. Our pentesters use manual exploitation to find what scanners can’t see, and every finding comes with evidence your developers can reproduce.
It’s written for two readers
Every finding is rated by business impact as well as technical severity. The executive summary tells your board why a specific finding matters; the technical report tells your developers how to fix it.
It ends with the fix
Each finding includes step-by-step remediation, and we walk your developers through the findings. A retest is available after your fixes, to confirm which findings are closed.
One attack path from a real engagement
Top row: the intended route. Bottom row: direct server access bypassed the SSO gateway. Read this case study.
We work for
- Financial & Banking Sectors (FinTech)
- SaaS & Cloud Providers
- Critical Infrastructure
- E-commerce
Not in one of these sectors? The method stays the same; only the scope changes to fit your systems.
Questions before you sign
Which standards do we follow?
Our methodology is aligned with the OWASP Web Security Testing Guide, the Penetration Testing Execution Standard (PTES) and NIST SP 800-115. Red team and TLPT work is aligned with MITRE ATT&CK. When a test supports a regulatory requirement such as PCI DSS 11.4, DORA or NIS2, we map the findings to it. The report is evidence for your own risk assessment and for your auditor.
What do you receive?
An executive summary for management that explains business risk in plain language, a technical report for your IT team listing every vulnerability with evidence of exploitation and remediation steps, and a retest available after your fixes, confirming which findings are closed. See the structure in our sample penetration test report.
Where do we work?
Pentestica is an EU-based company with clients worldwide, including the US and UK. Web applications, APIs, cloud environments and external infrastructure are tested over the internet, and access for internal testing is agreed during scoping.
What happens after the test?
We walk your developers and IT staff through the findings, so they understand how each attack worked and how to keep the same class of bug out of future releases. We also run security awareness training, and we provide cybersecurity consulting, from vCISO support and risk assessments to tabletop exercises and threat modeling.
Who do you sign the contract with?
You sign with Pentestica, an EU-based company. Legal entity details are in our privacy policy, and governing law is set out in the contract.
Can you speak to a past client?
Yes. References are available under NDA.
Which currencies do we invoice in?
Invoicing is in USD, EUR or GBP.
What language are reports in?
Reports are in English by default; other languages can be discussed.
When can testing start?
The start date is agreed with your quote.
Ask for a fixed price in writing
Tell us what you need tested. You get the scope, the tester-days and a fixed price for that scope before any testing starts.
Prefer email? hello@pentestica.com