
FIXED-PRICE QUOTE
Request a Penetration Test Quote
Tell us what needs testing. You get a written scope, tester-days and a fixed price before any testing starts, with no hidden fees.
Use the form to list what’s in scope (applications, APIs, networks or cloud accounts), your deadline and any compliance requirement the report has to support.
Tell us what needs testing. You get a written scope, tester-days and a fixed price before any testing starts.
- Fixed price from $2,500
- NDA and indemnity insurance
- 25 certified senior pentesters
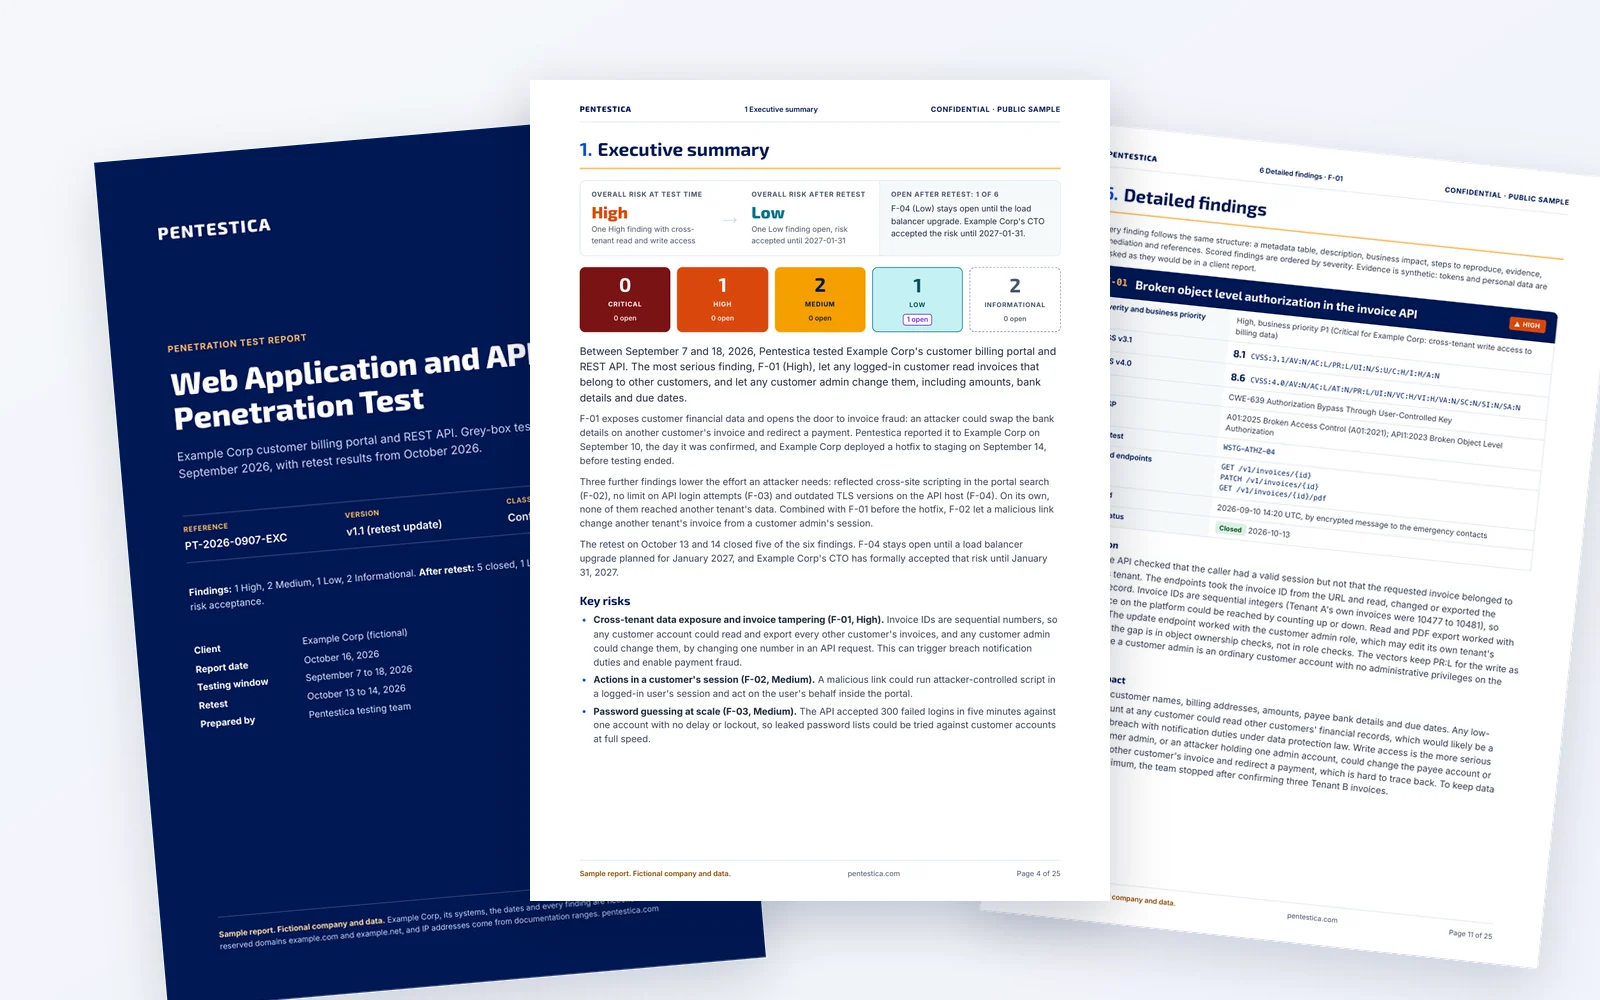
- See a sample report (opens in a new tab)
Written scope and fixed price before testing starts.Web app and API tests from $2,500.
NDA available before you share details.We carry professional indemnity insurance.
Retest available after fixes.25 certified senior pentesters (OSCP, OSCE, CISSP).
Request received
We’ll reply by email from hello@pentestica.com with scoping questions or a fixed quote in tester-days. If you don’t see it, please check your spam folder and add our address to your contacts.
Need an NDA first? Say so in your reply and we’ll sign one before you share more detail.
While you wait:
Prefer email? Write to hello@pentestica.com
Written scope and fixed price before testing starts.Web app and API tests from $2,500.
NDA available before you share details.We carry professional indemnity insurance.
Retest available after fixes.25 certified senior pentesters (OSCP, OSCE, CISSP).
Global Reach
Clients worldwide, including the US and UK
Invoicing in USD, EUR or GBP
What happens after you send the form
Every engagement starts the same way, so you know the scope and the price before any testing begins.
1. We read your scope
We reply by email with scoping questions or a fixed quote in tester-days. We ask what is actually in scope: which applications and APIs, how many endpoints and user roles, which environments, and whether the test has to satisfy a regulation such as NIS2, DORA, PCI DSS or HIPAA.
2. You get a written proposal
Test type, tester-days, timeline and one fixed price for the agreed scope, in writing. We sign an NDA before testing if you need one. See how penetration testing is priced.
3. Testing starts after written authorization
Rules of engagement define scope, timing, limits and contacts on both sides. Nothing outside that document is touched. Critical findings are reported during testing.
Who will test your systems?
Pentestica’s penetration testing team is made up of 25 certified senior pentesters who hold credentials such as OSCP, OSCE and CISSP and have 500+ penetration tests behind them. We design each scope around your technology stack and budget and explain the results in plain business language, as our sample pentest report shows. Our testing is aligned with OWASP WSTG, PTES and NIST SP 800-115.
What we need to quote a penetration test
To quote a penetration test, Pentestica needs the size of the scope (applications and user roles, API endpoints, IP ranges, hosts or cloud accounts), which environment to test, your testing window, any compliance requirement and whether you want a retest after fixes.
| Test type | What to send |
|---|---|
| Web application | Number of applications and user roles, roughly how many pages or features |
| API | Endpoint count, authentication type (OAuth 2.0, API keys, JWT) and any OpenAPI or other documentation |
| Mobile app | Platforms (iOS, Android or both), user roles and the API the app calls |
| External network | Public IP ranges, domains and subdomains in scope |
| Internal network | Approximate number of hosts, sites and Active Directory domains |
| Cloud (AWS, Azure or GCP) | AWS accounts, Azure subscriptions or GCP projects, and the main services you use |
For every test, also tell us:
- Environment: production or staging.
- Testing window: dates that suit you and any hard deadline.
- Compliance requirement: PCI DSS v4.0.1, NIS2 (Directive (EU) 2022/2555), DORA (Regulation (EU) 2022/2554), HIPAA or GDPR, if the report must serve as evidence.
- Retest: whether you want a retest after fixes.
Missing details are fine; the scoping questions in step 1 above fill the gaps.
How we price: tester-days and a fixed price in writing
Pentestica prices each penetration test in tester-days, the days certified pentesters need to test the agreed scope by hand. Those days become one fixed price for that scope, confirmed in writing before testing starts, with no hidden fees. Scope, complexity, testing approach, compliance reporting and retesting decide where a quote lands in its range.
| Test type | Published range (USD) |
|---|---|
| Standard web application or API | $2,500–$5,500 |
| Mobile app (iOS or Android) | from $3,500 |
| Complex infrastructure or cloud (AWS and Azure) | $5,000–$12,000+ |
| Red teaming | from $15,000 |
| Full DORA threat-led penetration test (TLPT) | Quoted individually |
| External-only or internal-only network test | Quoted individually |
Beyond what step 2 lists, the written proposal states:
- Scope: the systems, user roles and environment the price covers, and the testing approach (black, gray or white box).
- Deliverables: an Executive Summary for management and a Technical Report for IT with the vulnerability list, exploitation evidence and step-by-step remediation.
- Retest: a retest is available after fixes.
Our guide to penetration testing cost explains what each range covers; your quote turns the range into one fixed number.
How to compare penetration testing quotes
Compare penetration testing quotes on what the price buys, not on the total. Check five things in each quote: the scope and its assumptions, the number of tester-days, the share of manual testing, a sample report with exploitation evidence, and the retest terms.
| Criterion | What to check | How Pentestica handles it |
|---|---|---|
| Scope and assumptions | Which systems, roles and environments are priced, plus exclusions and assumptions | A proposed scope in writing; nothing outside the written authorization is tested |
| Tester-days | How many days of testing the price buys; a lower total can mean fewer days | Tester-days stated next to the fixed price |
| Share of manual testing | How much of the effort is hands-on testing rather than automated scanning | Manual testing by certified pentesters |
| Sample report with evidence | Reproduction steps, exploitation evidence and specific remediation for each finding | Our sample penetration test report (its evidence is synthetic; client reports carry the real traces) |
| Retest terms | Whether a retest after fixes is offered, what it costs and how many rounds it covers | A retest is available after fixes; ask for its terms |
If a quote leaves any of these vague, ask before you sign. The same five questions apply to ours. Benchmark the numbers you receive against our penetration testing cost benchmarks before you decide.
Frequently asked questions about pentest quotes
Can I get a penetration testing quote by email?
Yes. Send the scope through the form above or to hello@pentestica.com. Our answer comes by email: either a few questions about the scope or a fixed price in tester-days. Not sure what to include? Our guide to penetration test scope lists what goes in, what stays out and what to send.
Will you sign an NDA?
Yes. We sign an NDA before testing, and before you share a detailed scope if you prefer.
Do you carry insurance?
Yes, we carry professional indemnity insurance.
Do I have to get on a call?
Not to request a quote: the form or an email is enough. Some scopes are quoted after a scoping call. Either way, you get a written scope, tester-days and a fixed price before any testing starts. Work outside the agreed scope can cost more.
Do you test production systems?
Yes. Production and staging both work, and the environment is agreed during scoping. We monitor system stability in real time and agree a testing window with you; if anything degrades, testing stops and we alert your emergency contact.
Should I ask for black box, gray box or white box testing?
For most applications, gray box testing (credentials plus documentation) is the most efficient choice. Black box spends tester-days on reconnaissance, while white box (source code access) finds the most and takes the longest. If you’re unsure, say so in the form, and the proposal will recommend an approach and price it in tester-days.
Ready to send your scope?
A few lines are enough to start. You get a written scope and one fixed price before any testing begins.
Or email hello@pentestica.com